What it demonstrates
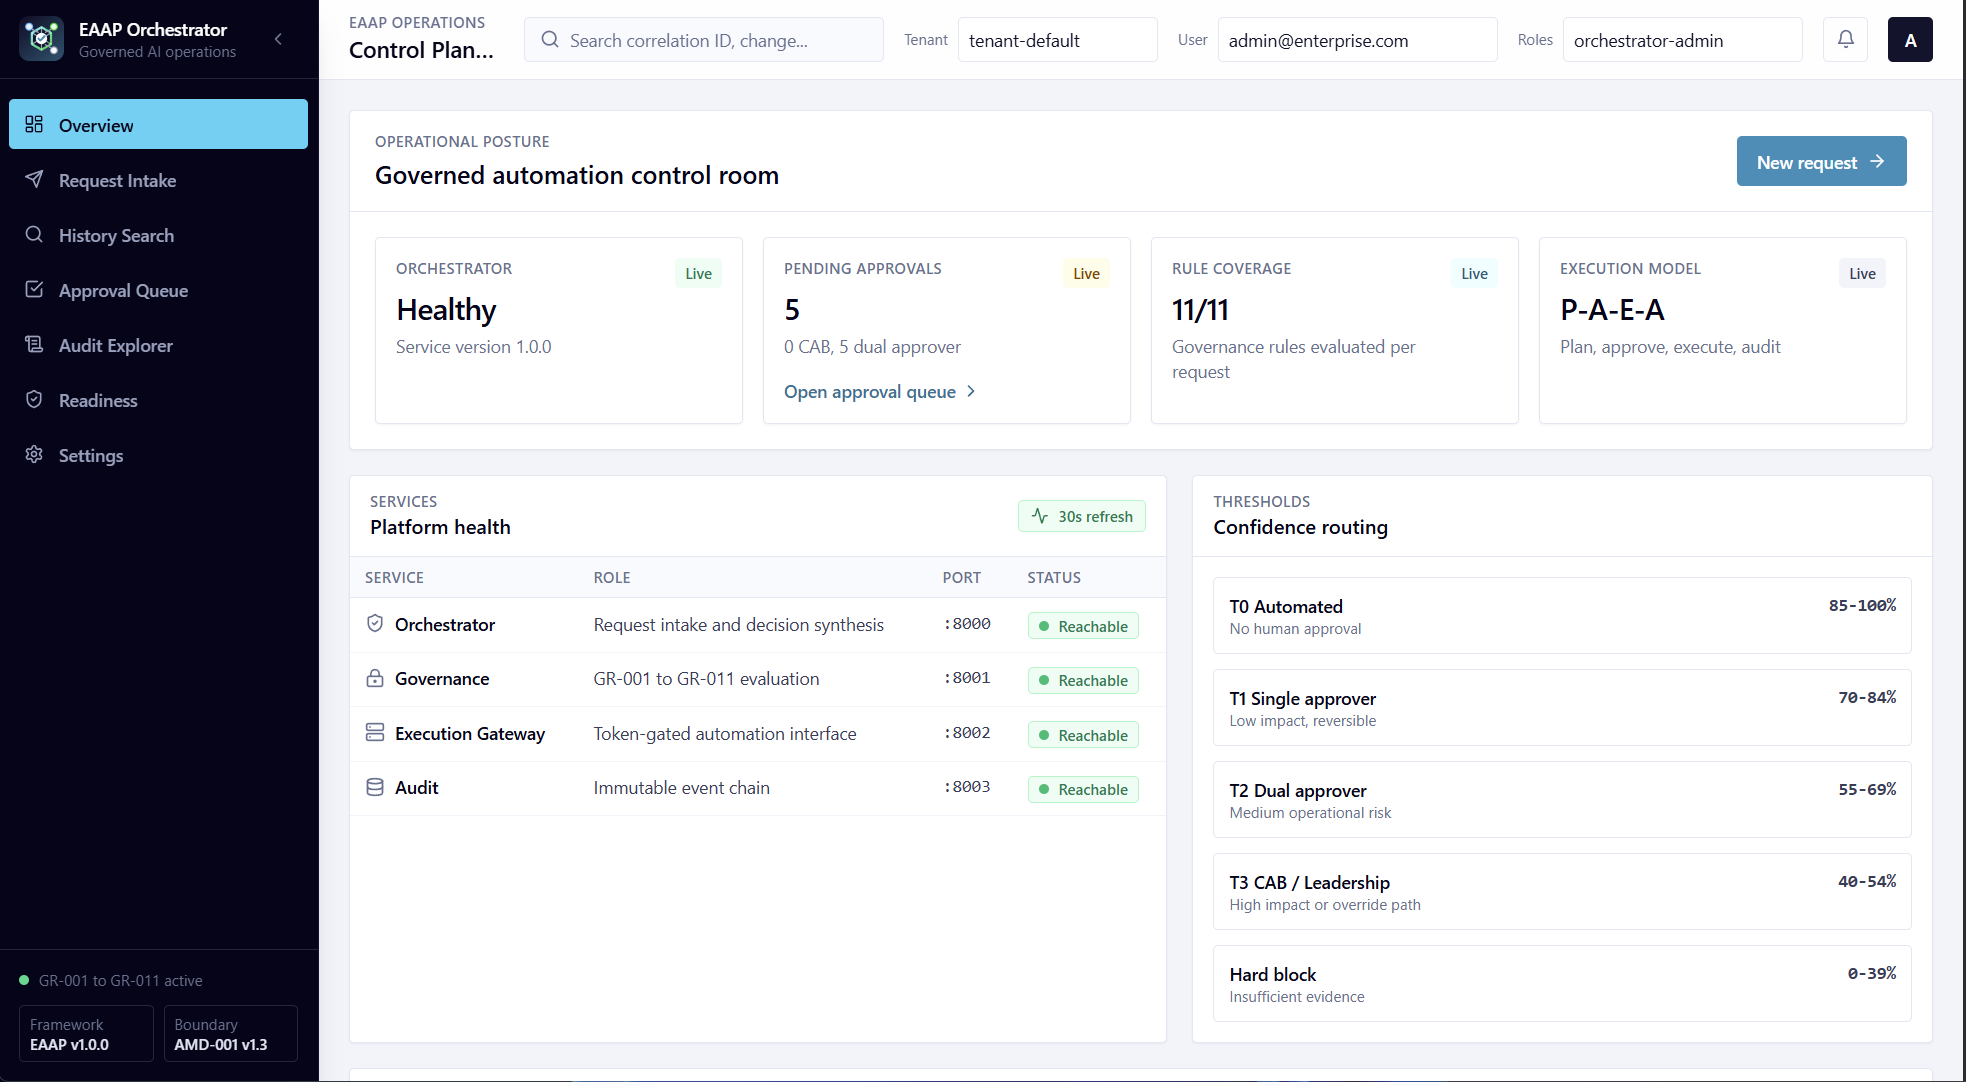
The project explores a plan, approve, execute, audit operating model where AI can recommend, but deterministic controls, persistent token state, approval quorum, release gates, and audit-chain checks decide what may proceed.
Current evidence
- Public source repository with STATUS maturity boundary updated Aug 23, 2026.
- Verified check-suite expectations cover pytest, ruff, bandit, UI type-check/build, Docker Compose config, migration validation, Kubernetes manifest validation, production-runtime validation, and control-plane smoke testing.
- Docker Compose smoke evidence covers service health, approval quorum, post-approval token issuance, gateway execution by server-side token ID, required audit events, audit-chain integrity, and fail-closed token issuance before approval quorum.
- Token persistence, release-gate hardening, local users demo flows, OpenAPI contracts, HLD, ADRs, threat model, and maturity boundaries are documented.
- Published Zenodo research connected through ORCID.