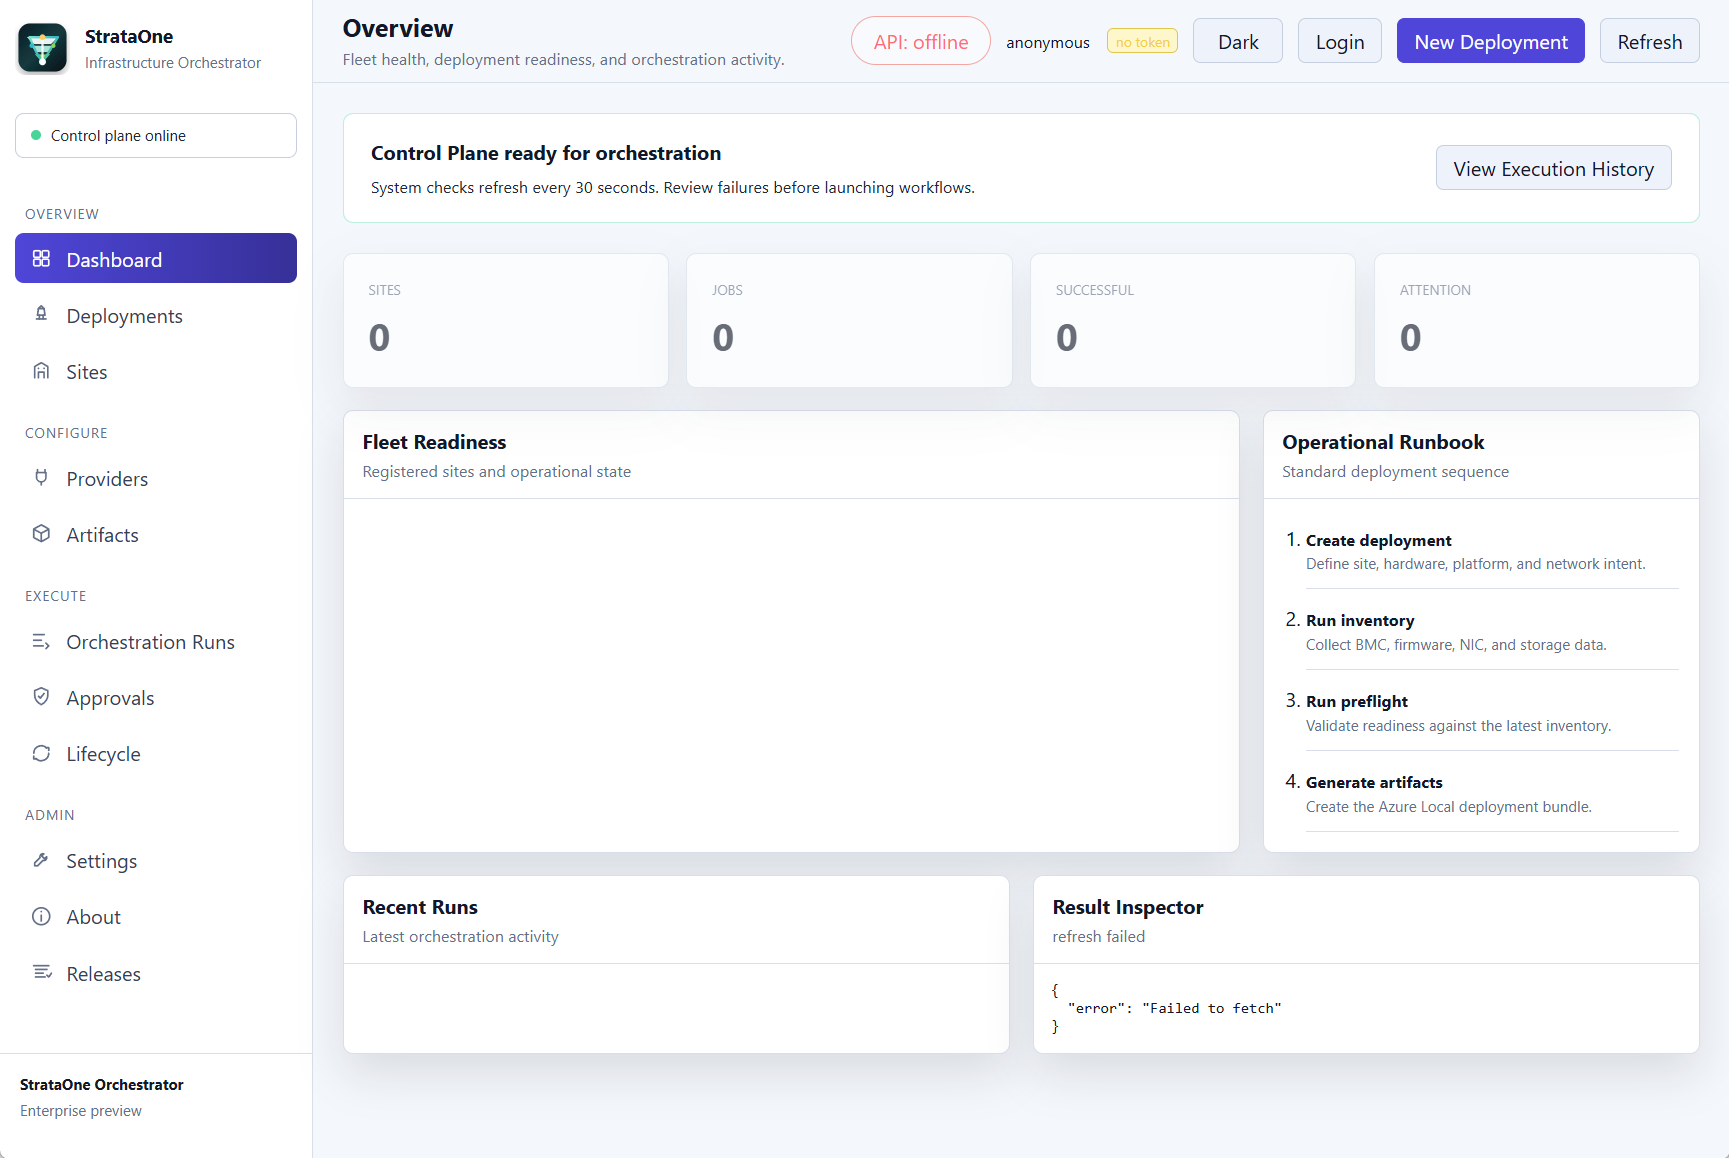
What it demonstrates
The project explores a broader orchestration pattern where the console shape is inspectable and the implementation boundary remains explicit. The current repo baseline includes production-control-plane hardening, Azure Local provider handoff artifacts, an azure-local-execution-manifest.json handoff record, a ready-for-provider-handoff state, approval-gated live Redfish operation boundaries, queued job credential guards requiring credential references or a secret provider, SBOM generation and attestation, Trivy container vulnerability scanning with high/critical fixable-CVE gates, and OEM validation signals. The Azure Local path is represented as provider-ready handoff evidence, not live Azure mutation from the demo.